
BlueUPALM: Banking-grade AML/DORA platform
Application for the analysis and detection of information potentially derived from money laundering. It implements a Hybrid Asynchronous Authorization architecture that combines centralized governance with decentralized execution at the edge.
The platform in action, in four minutes

→ View full presentation with scene index
One system for compliance, IT and audit
Compliance officers
Analysts investigating suspicious activity and managing Anti-money laundering (AML) is the prevention of money laundering and terrorist financing. In Spain, Law 10/2010 requires credit and financial institutions to apply customer due diligence and to report suspicious transactions to SEPBLAC; Regulation (EU) 2024/1624 harmonizes it from July 2027.Read more → AML alerts.
System administrators
IT staff managing access policies, hybrid auth and edge deployments.
External auditors
Regulators reviewing compliance logs and immutable audit trails.
Detect at the edge without losing the audit trail
Real-time threat detection
Identify and block suspicious transactions with ultra-low latency.
Immutable auditing
Maintain cryptographic logs of all actions and decisions for compliance.
Secure edge operations
Enable autonomous agent operations in decentralized environments securely.
See the risk, read the policy, control who has access
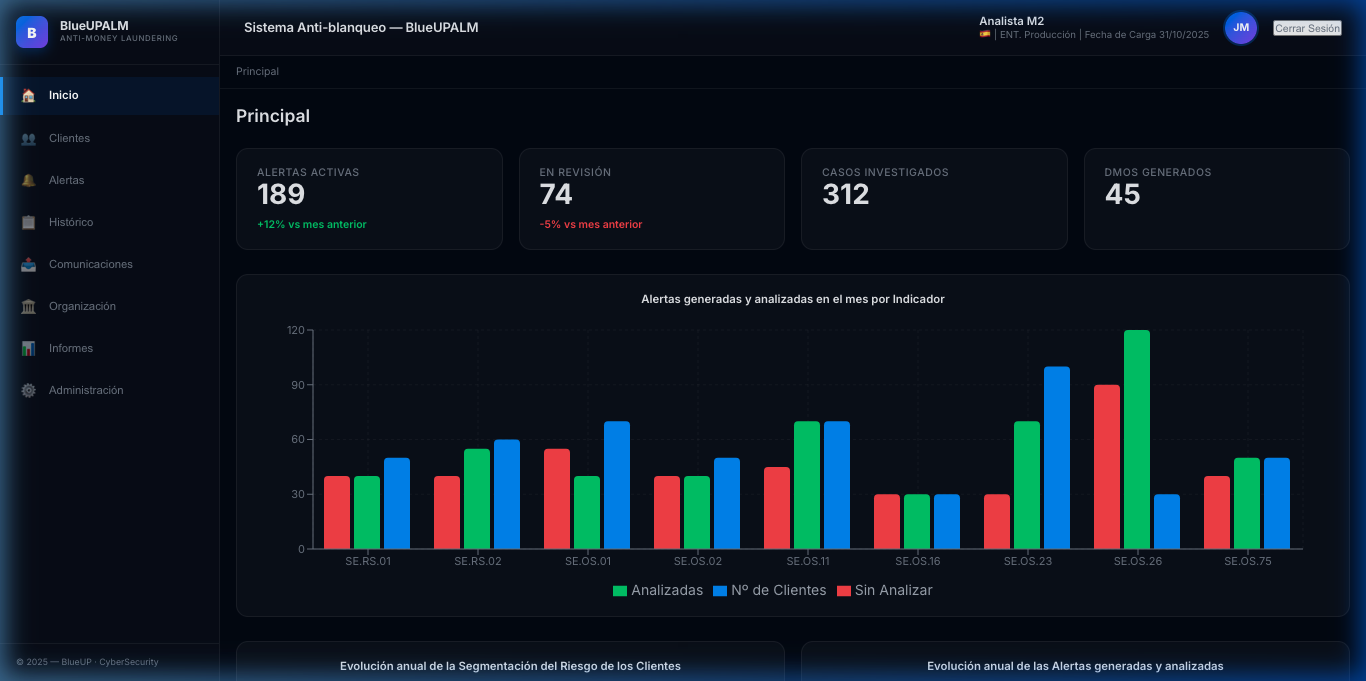
- Risk Dashboards — Visual analytics of flagged transactions and risk scores
- Policy Management UI — Read-only view of the centralized Cerbos policies (application layer), versioned through GitOps
- Identity & Access Control — Granular control over Ziti identities (device provisioning and approval), Keycloak users and network access
Low latency, outage tolerance and the data perimeter
Ultra-low latency
Edge verification with minimal delay in transaction processing.
High resilience
System must remain operational during network fluctuations (offline capability).
Data perimeter
Sensitive PII and financial data is processed within the authorized perimeter, except in AI triage, which sends the alert context, including the client's document identifier, to an external model provider.
Declared limits
What BlueUPALM does not do yet, or does only in part, with the status its source repository gives it: operational, modelled or roadmap.
- AI triage governance: validation of every agent decision against the Cerbos policy engine (PDP) is operational when
CERBOS_URLpoints to a deployed Cerbos, as in the reference stack. Without that variable, the agent resolves with embedded local rules, a development fallback that is neither the PDP nor the versioned policy; with the variable set, a connection failure to the PDP degrades to the same fallback request by request. - Model reasoning audit: roadmap. Reasoning-trace capture for the LLM (Langfuse) is in the design and has no deployment.
- Agent service identity: modelled. SPIFFE/SPIRE is present in the triage agent configuration, but the identity it presents to the PDP is the literal
ai-triage-agent, not an SVID issued by SPIRE. - Policy management from the interface: modelled. The Cerbos policy editor and policy list exist as read-only components and are mounted today only in the screenshot application, not in the main application routing.
- Sanctions screening: operational with a local three-level matching engine (exact, alias and fuzzy) and EU, OFAC and UN list updates from OpenSanctions. Integration with commercial list providers (Dow Jones, Refinitiv) is roadmap.
- DMO reporting to SEPBLAC: the API exposes DMO file queries and F19 PDF downloads; the frontend DMO management screens read demonstration data, and generating the file and submitting it to the Servicio Ejecutivo are roadmap: what exists today is the typed data model of the DMO file and its operations, and the special examination flow that leaves the case marked as generated.
- DORA incident reporting to the supervisor: the platform classifies the incident, generates the initial report draft (ITS 2025/302, Annex I) in PDF and XML and computes the 4-hour, 72-hour and 30-day deadlines; submission to the competent supervisor is roadmap.
Next steps to evaluate BlueUPALM
Commercial Demo
4-minute video presentation covering all features. → View demo
Regulatory compliance
DORA (Digital Operational Resilience Act) is Regulation (EU) 2022/2554 on digital operational resilience for the financial sector. It requires EU banks, insurers and investment firms to withstand ICT disruptions and threats, respond to them and recover. It has applied since 17 January 2025.Read more → DORA, SEPBLAC (Servicio Ejecutivo de la Comisión de Prevención del Blanqueo de Capitales e Infracciones Monetarias) is Spain's Financial Intelligence Unit and its supervisor for the prevention of money laundering and terrorist financing. Obliged entities file suspicious transaction reports with it (Law 10/2010).Read more → SEPBLAC, The GDPR (General Data Protection Regulation) is Regulation (EU) 2016/679 on data protection, applicable since 25 May 2018. It reaches every entity established in the EU and anyone outside it offering goods or services to people in the Union or monitoring their behavior. Fines run up to 20,000,000 EUR or 4%.Read more → GDPR and The AI Act is Regulation (EU) 2024/1689, the European risk-based framework for AI: it bans unacceptable uses, regulates high-risk systems and requires transparency from general-purpose models. Its high-risk regime covers credit scoring and life and health insurance pricing from 2 December 2027 (Reg. 2026/1744).Read more → AI Act — what BlueUPALM contributes to each regulation and what is roadmap.Screenshots
Full BlueUPALM frontend gallery with Dark Glassmorphism design. → View screenshots
Request demo
Personalized 30-45 minute session adapted to your sector and use case. → Request demo
See the real interface before the demo
Platform fit
BlueUPALM is the node with the most edges in the platform graph: it consumes the engine's ledger trail, resolves workstation enrollment and publishes the DORA alerts of its own compliance cycle. The platform architecture lays out the three layers and their order.
What it receives. From BlueUP Core (Financial engine), one canonical event per business event on the NATS subject blueup.core.ledger.events, to which it is already subscribed; none arrives today because BlueUP Core has no reference deployment on the platform. From BlueUP Connect (Zero Trust desktop client), the provisioning request and its status (provisioning.request, provisioning.status.{request_id}, provisioning.enrolled), resolved in the admin panel.
What it delivers. An HTTP API (/api/*) and the edge security service on :8080, which issues tokens over HTTP (/issue) and verifies them over NATS (verify.request); over NATS, DORA alerts (dora.alert.>), the regulatory KPI breach notice (alerts.regulatory.kpi_breach), triage responses (triage.response.>) and DORA assessment responses (dora.assessment.response.>). The other compliance product in the portfolio is ComplianceView (Compliance monitoring), which monitors compliance controls and consumes none of those subjects.
Talk to our team
The demo walks through BlueUPALM in a 30-45 minute session adapted to the institution's sector and use case.